For developers
Ship the site. Keep the browser under watch.
One response header collects CSP and browser security reports from your real traffic: violations to debug, alerts to act on. No agent, no SDK.
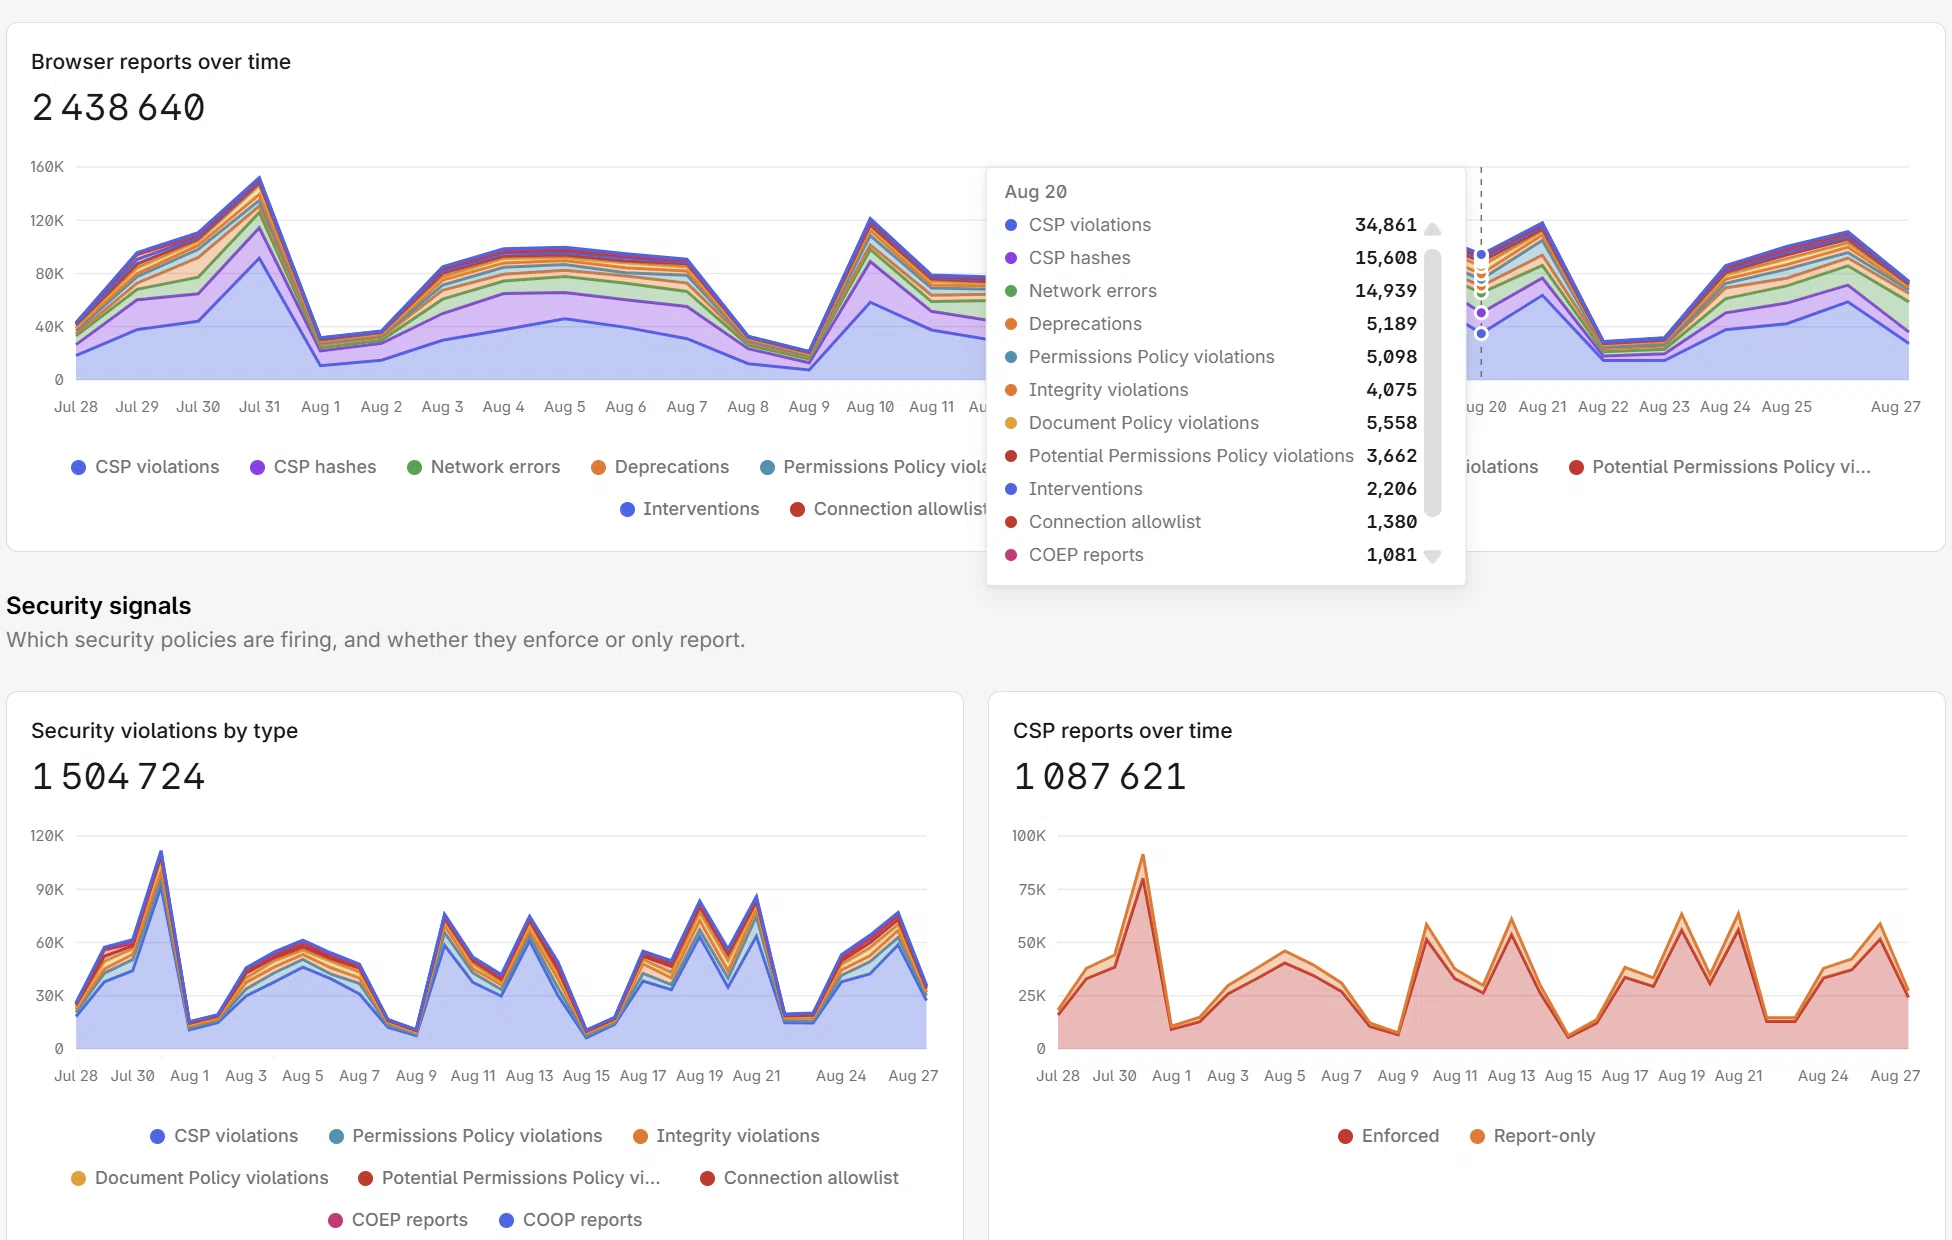
- 1.5B
- reports ingested
- 12
- report types collected
- 0
- agents or SDKs to install
- 100%
- EU data residency
The blind spot
Your server tools stop at the response.
Third-party scripts, injected code and policy violations execute in the browser, after the page leaves your infrastructure. CentralCSP collects the signal browsers already emit and routes it back to your stack.
01 - Browsers
Native Reporting-API signals from your real production traffic.


- csp-violation
- deprecation
- intervention
- network-error
- crash
Real production traffic
Reports come from your actual visitors' browsers, not a crawler pointed at a staging URL.
Source-level context
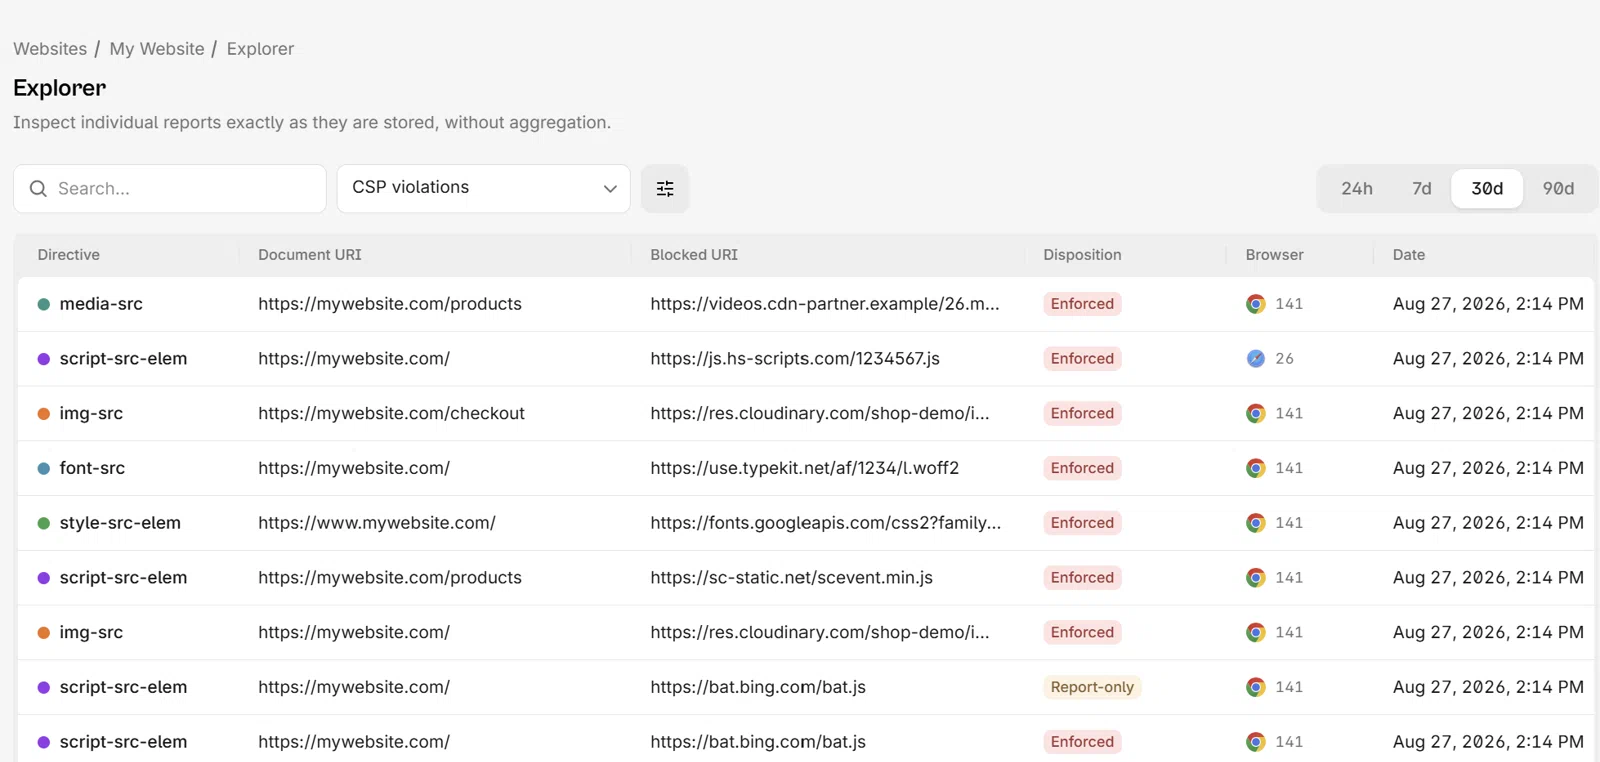
Every violation keeps its source file, line, column, directive, browser and origin.
Zero runtime dependency
Nothing loads on your pages. Browsers report natively, so performance impact is zero.
Setup
One header. That's the integration.
Ship it from the CDN, reverse proxy, framework or application layer, whichever you own.
Have a CSP already? Point its report-to at the same endpoint and every violation lands there too.
Add your site
Create the site in your dashboard and copy its managed reporting endpoint.
Ship the header
Deploy from your edge or app. Reports flow from real visitor browsers immediately.
Route the signal
Watch the live dashboard, wire alerts to your channels, pull anything over the API.
Free tools
Try the full security toolkit.
Six tools, no account required. The same engines the platform runs on.
CSP scanner
Map the headers, policy findings and reporting coverage of any public site.
- Full header inventory
- Findings ranked by severity
- Results on a shareable page
CSP evaluator
Paste a policy and get prioritized findings with a clear score.
- Directive-by-directive findings
- A clear overall score
- Powered by the platform engine
Reporting-API checker
See which reports a site actually collects, and where they are sent.
- Endpoint and binding checks
- Coverage per report type
- Dropped-report warnings
Security headers scanner
Audit the response headers of any public site and see what's missing.
- Every header, graded
- Fixes for what's missing
- Rescan after you deploy
Security compare
Scan your site live and see how it ranks against your industry.
- Live scan of your site
- Industry cohort comparison
- Assess your maturity
Chrome extension
Watch live violations and build or test a policy against any page in your browser.
- Live violation feed
- Build and test policies in place
- Works on the page you're viewing
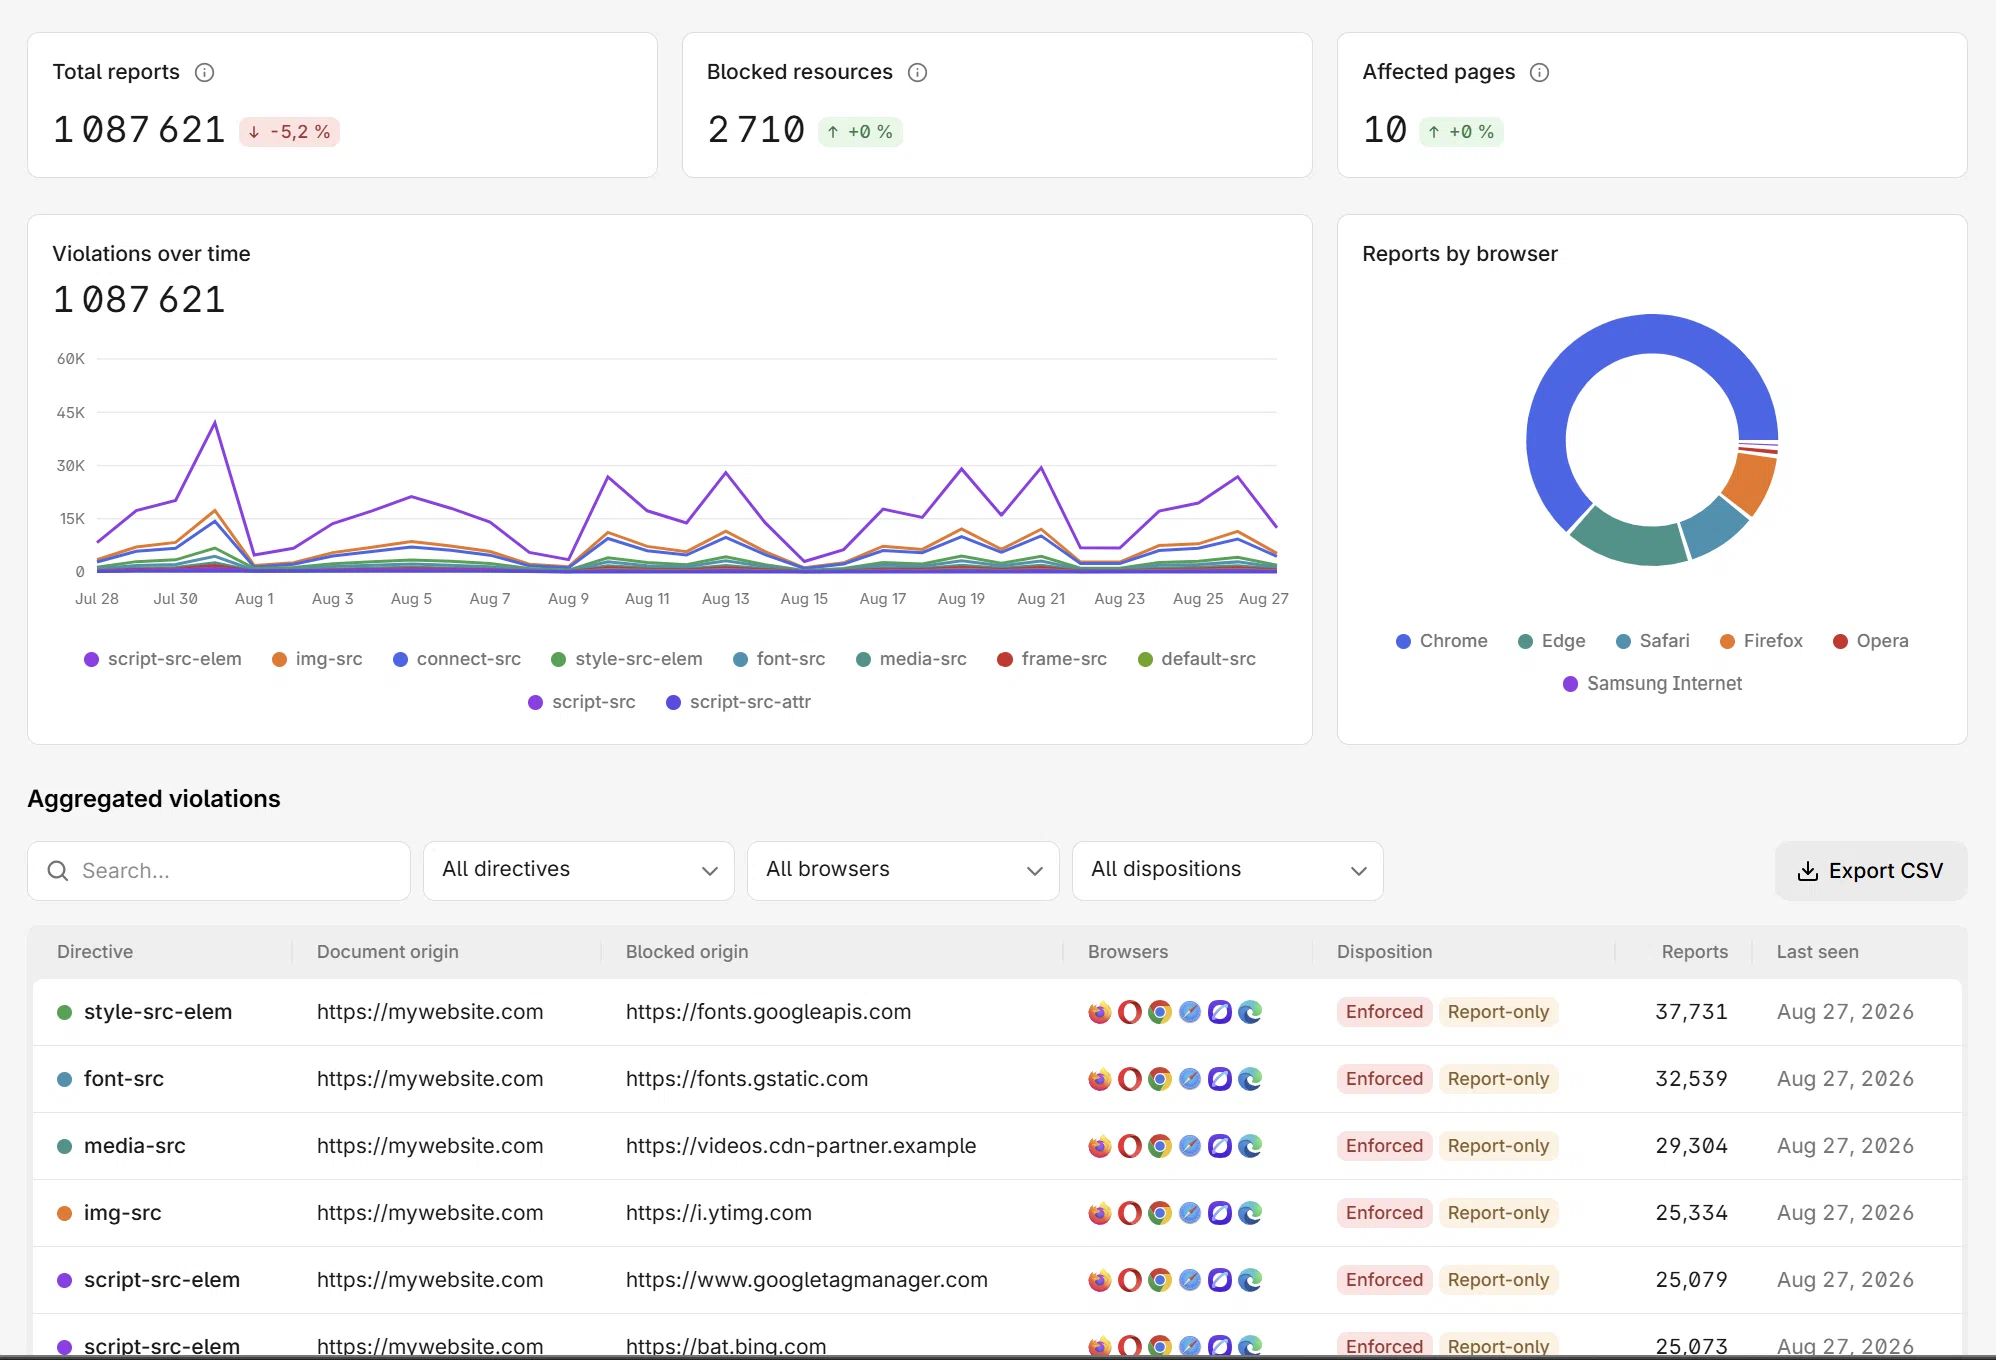
The dashboard
Everything happens in one place.
Reports, scores, inventories and evidence for every site you ship, behind one login.
Automation
Everything in the dashboard, over the API.
Reports, inventories, scores and evidence are all queryable. Automate site onboarding, export everything, or let your AI agents drive it over MCP.
- Full REST API with workspace API keys
- Webhooks, CSV and raw-report exports
- Built-in MCP server for AI agents
- Alerts to Slack, Teams or any webhook
Past the code review
Answers for the rest of the room.
What compliance, security review and procurement will ask about, covered by the same platform.
01 - Compliance
PCI DSS evidence
If your checkout is in scope, requirements 6.4.3 and 11.6.1 are covered from the same signal.
02 - Security review
Enterprise controls
The controls your security review asks about, already in place. Data hosted in France, on OVH.
03 - Access
Team and access
Bring the whole team without sharing one login, and scope who sees what.
Pricing
Priced for a side project. Built for production.
Start covers real collection on your first production site: every report type, the live dashboard and unlimited scans. Upgrade when you need automation.
- 12 report types, one header
- Unlimited scans
- Policy builder
- 14-day free trial
Start
For a first production site.
- Applications3
- Users5
- Reports / month250,000
Plan features
- Full Reporting-API support
- Unlimited scans
- Script inventory
- Team access and RBAC
- Policy builder
The signal
The reports you will read first.
One endpoint collects all twelve types. These are the three most developers open on day one.
csp-violationView docsCSP violations
A resource was blocked, or would be blocked, by your Content Security Policy.
csp-hashView docsScript hashes
The hash of every script the page executes, the raw material for hash-based policies.
network-errorView docsNetwork errors
DNS, TLS and connection failures your server never sees, logged by the browser itself.
FAQ
Frequently asked questions
Implementation, safety and automation, answered.
Add the header. See what the browser sees.
Start with one site and real production traffic. 14-day free trial, no agent to deploy.