For agencies
Every client site. One security dashboard.
Monitor the scripts, policies and headers of your whole portfolio from one place, and turn client-side security into a service your clients pay for. EU-hosted.
Fifteen sites is fifteen attack surfaces
No time to babysit
You ship sites weekly. Nobody on the team has hours to review raw violation reports per client.
Clients want proof
"Are we secure?" deserves better than a shrug. You need something credible to show, in plain words.
PCI landed on your desk
Your merchant clients forward the auditor's questionnaire to you. 6.4.3 and 11.6.1 are now your job.
For your portfolio
Agency features, built in.
Everything you need to run security for a book of clients, included in one plan.
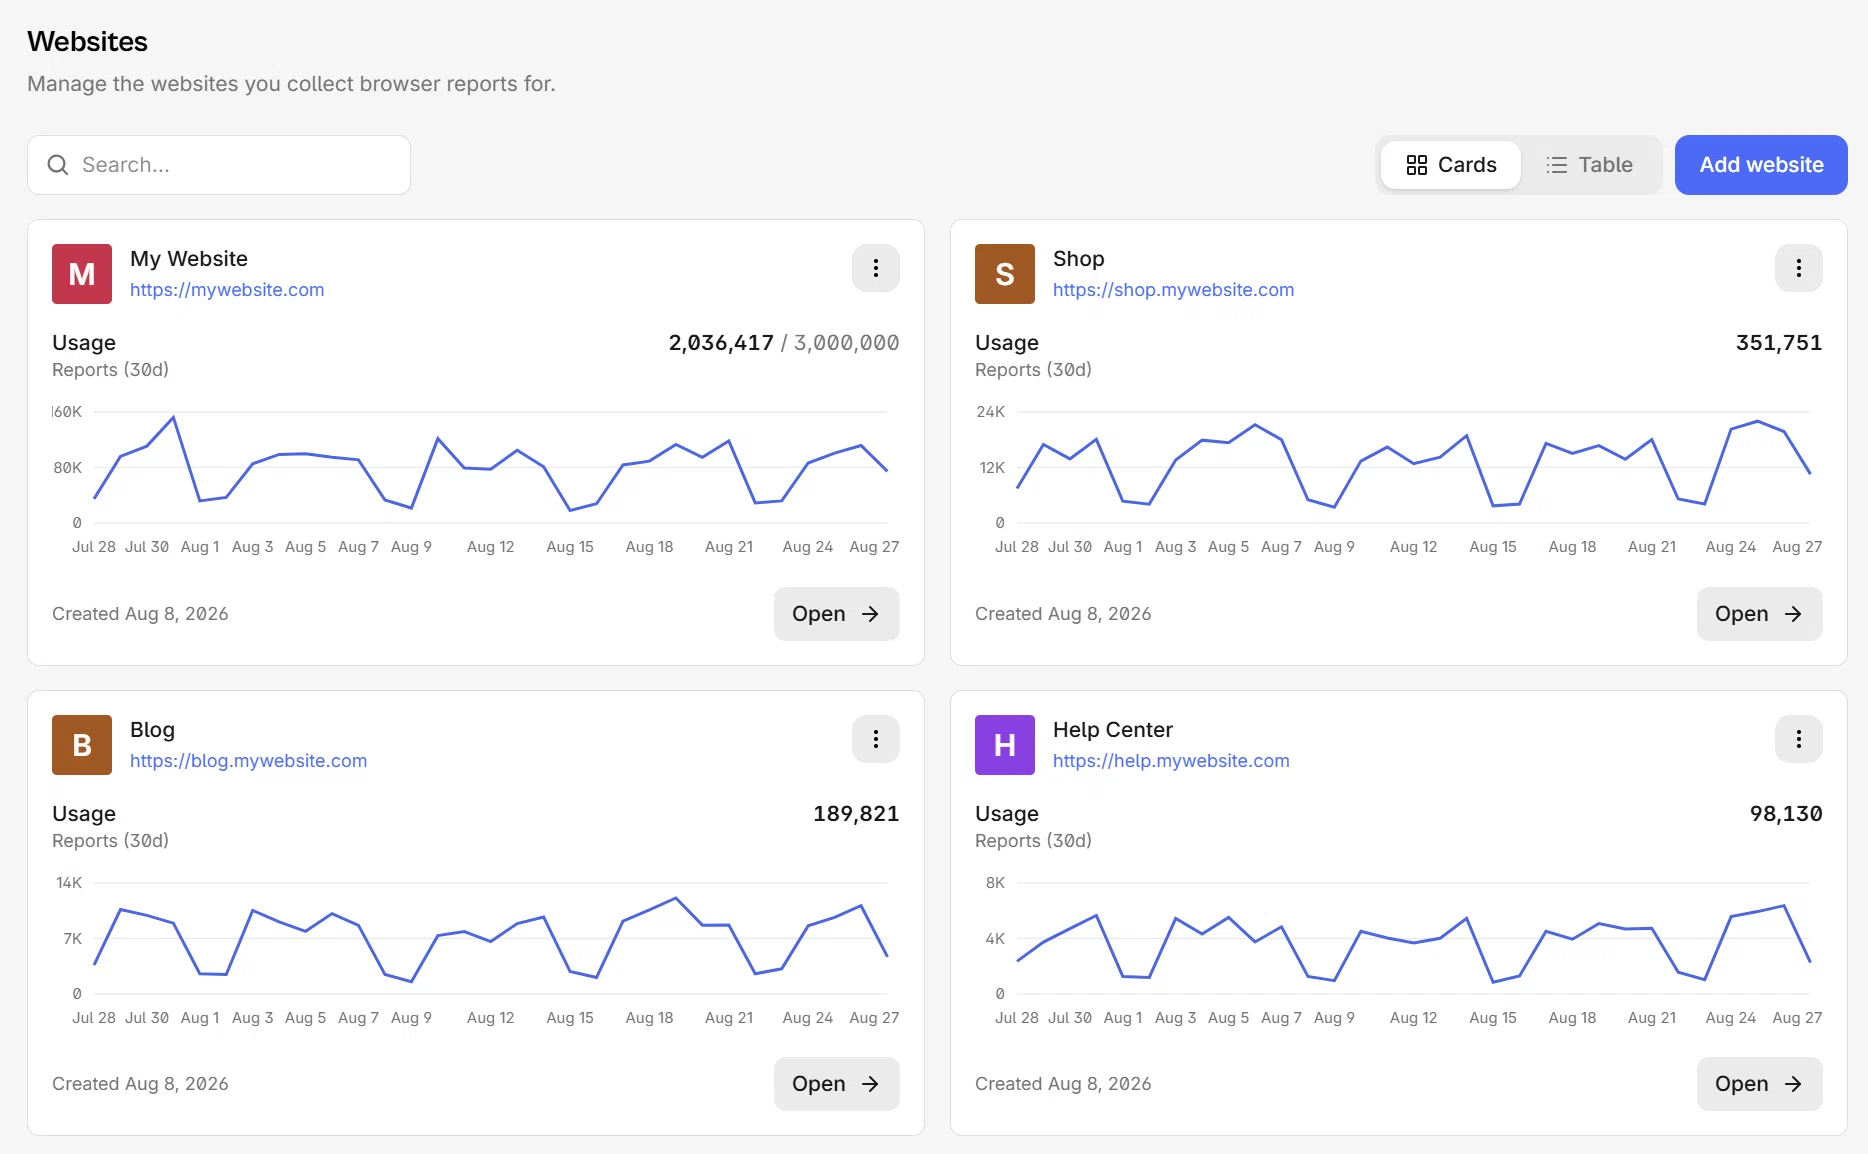
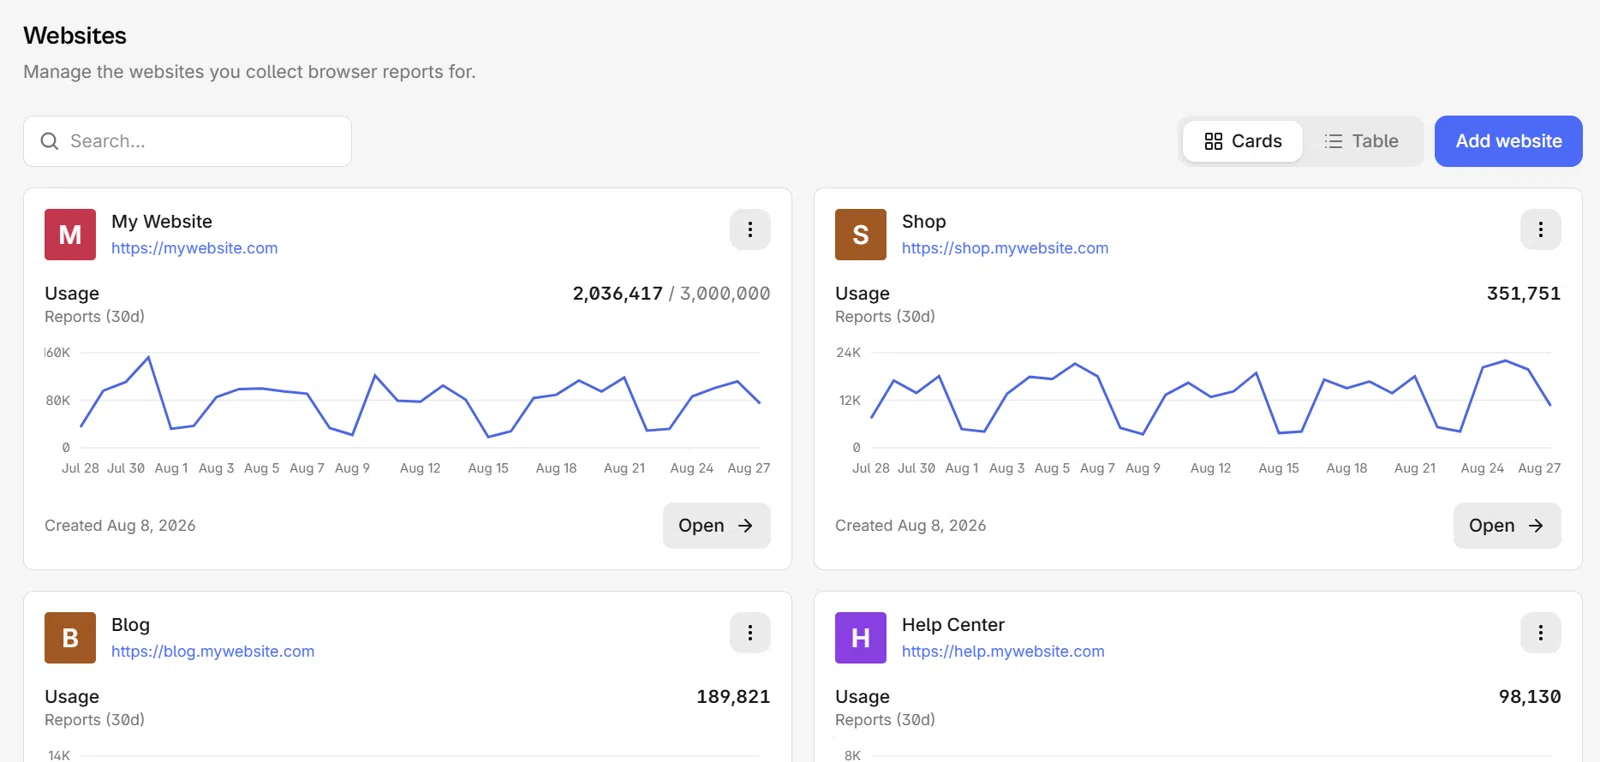
Your whole portfolio, at a glance
Every client site on one screen: security score, report volume, open advisories. Green means move on. Red means you knew before the client did.
- Health and score per site
- CVE flags on client scripts
- Drill into any site in one click
Scoped to how agencies work
Access scoped per site, alerts routed per team. Your juniors see the sites they work on, not your whole book.
- Roles scoped per member and per site
- Team access without shared logins
- Alert channels per site
Nothing to install
One response header per client site and reports flow from real visitor browsers.
- 12 report types, one endpoint
- Real production traffic
- Zero performance impact
CSP builder
Build and refine each client's policy from what their traffic actually loads.
- Generated from real reports
- Report-only first, enforce when clean
- Catches what a crawler misses
PCI DSS evidence
Auditor-ready 6.4.3 and 11.6.1 evidence for every merchant client.
- Payment-page script inventory
- Justification workflow
- Auditor-ready exports
Supply-chain
Know every script your clients ship, and get flagged the moment one gains a CVE.
- Script SBOM per site
- Known-CVE detection
- New-script alerts
How it works
A new client takes five minutes
No agent, no SDK, no code changes on client sites. Browsers report natively.
01 - Add
Create the site in your dashboard.
Add each site, invite your team, set who sees what.
02 - Connect
Paste one response header.
Reports start flowing from real visitor browsers immediately. Zero performance impact.
03 - Deliver
Route alerts, share the evidence.
Send each client's incidents to the right channel and forward monthly proof that their site is watched.
'%20gradientUnits='userSpaceOnUse'%3e%3cstop%20offset='0'%20style='stop-color:%235a62c3'/%3e%3cstop%20offset='.5'%20style='stop-color:%234d55bd'/%3e%3cstop%20offset='1'%20style='stop-color:%233940ab'/%3e%3c/linearGradient%3e%3cpath%20d='M21.8%20125h218.3c12.1%200%2021.8%209.8%2021.8%2021.8v218.3c0%2012.1-9.8%2021.8-21.8%2021.8H21.8C9.8%20387%200%20377.2%200%20365.2V146.8c0-12%209.8-21.8%2021.8-21.8'%20style='fill:url(%23microsoft-teams_svg__SVGID_1_)'/%3e%3cpath%20d='M188.4%20208.1h-43.6v118.8H117V208.1H73.5V185h114.9z'%20style='fill:%23fff'/%3e%3c/svg%3e)


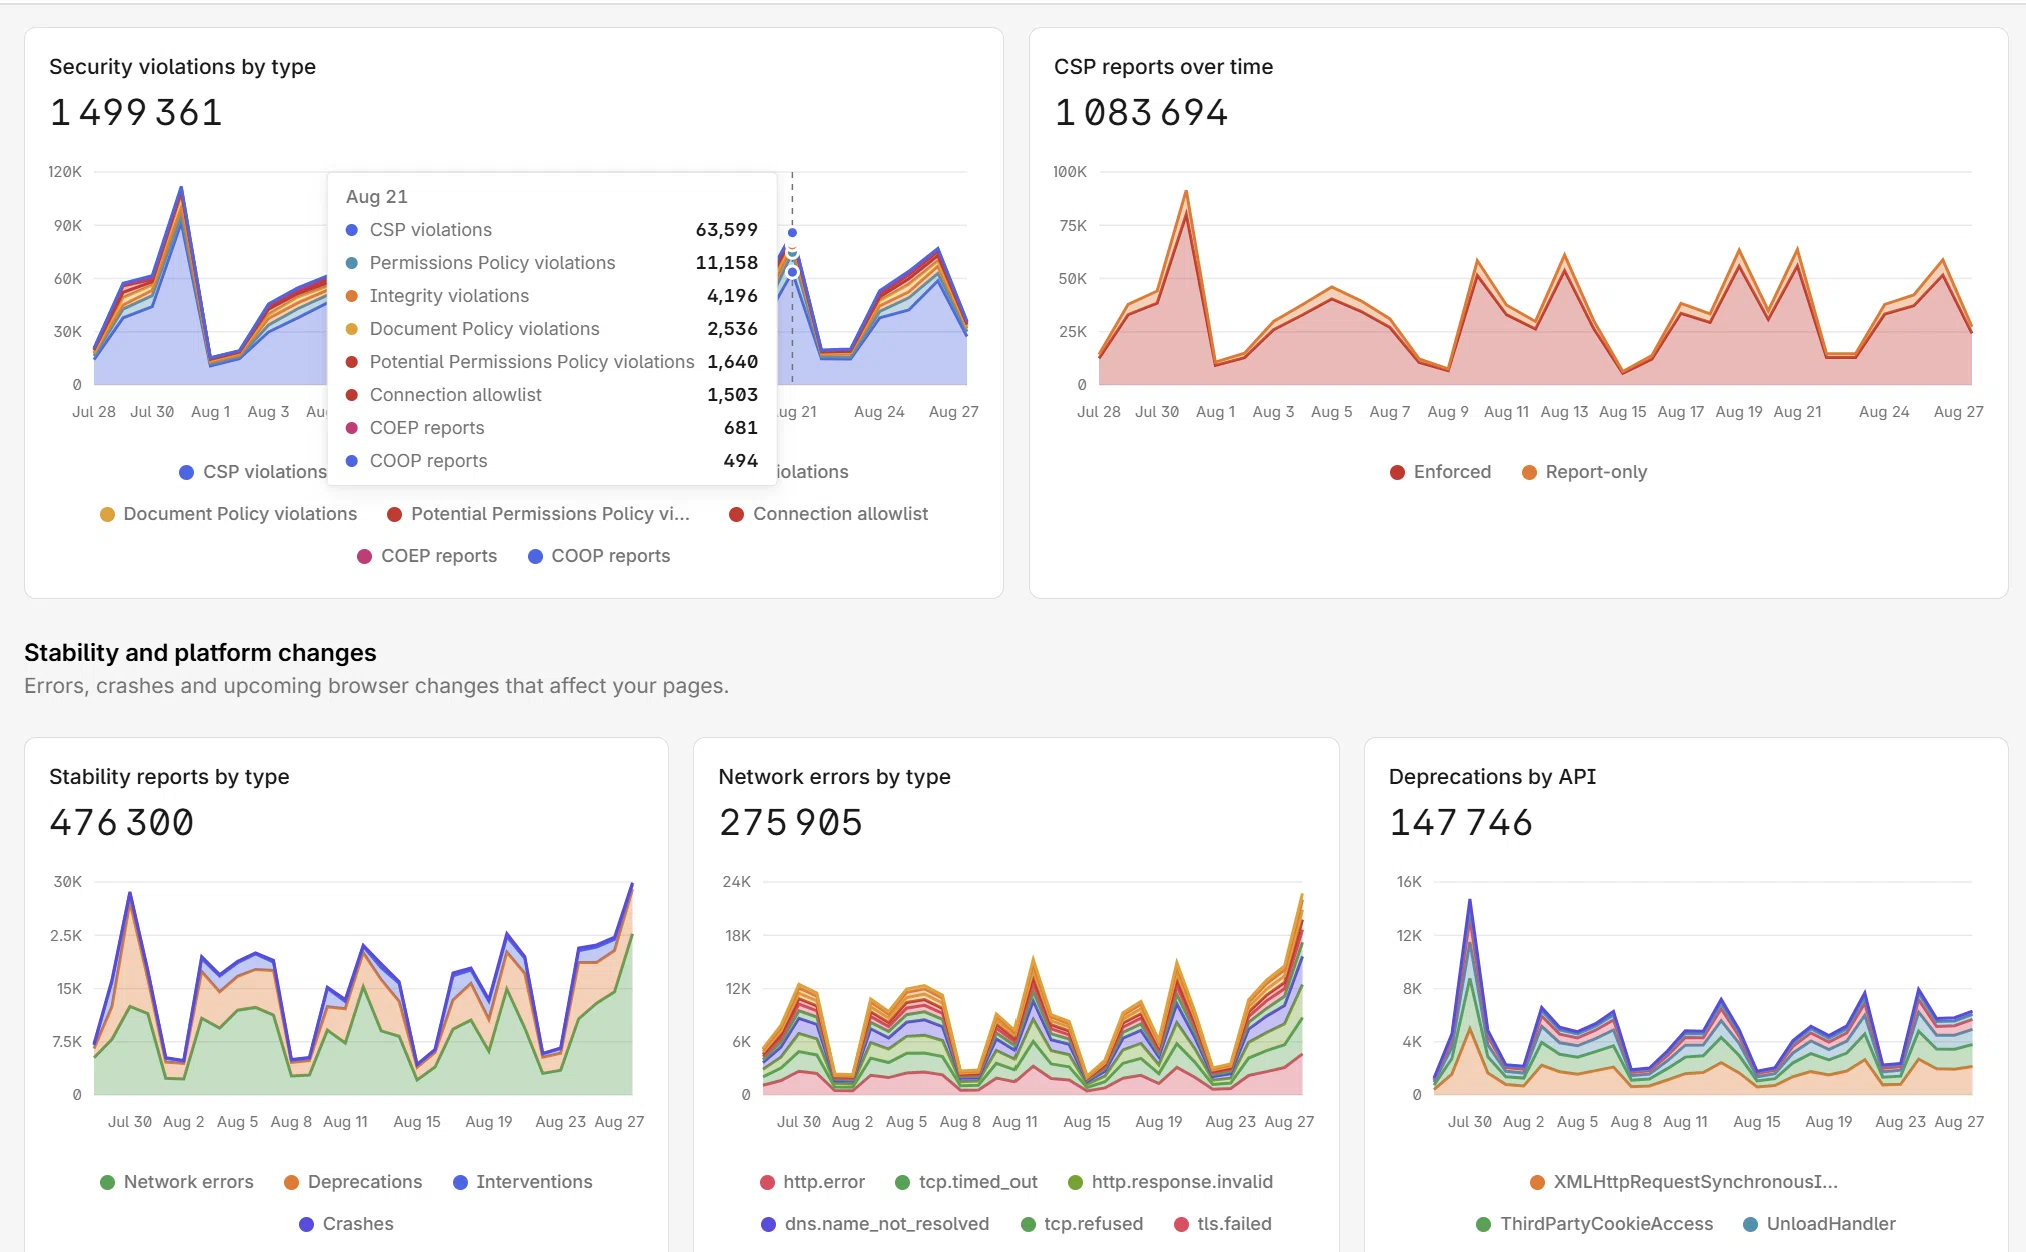
The dashboard
Everything happens in one place.
Reports, scores, alerts and evidence for every client site, behind one login.
- 250+
- agency sites monitored
- 1.5B
- reports ingested
- 82.5k
- websites analyzed
- Full
- Reporting-API support
Pricing
One subscription. A line item in every care plan.
Business covers your whole portfolio in one dashboard: automated scanning, API & MCP and alerting are all in the plan. Resell the monitoring to each client at your own rate.
- Every client site in one dashboard
- Automated scanning on every site
- Alerting, API and MCP included
- EU-hosted client data
Business
Automate it and wire it into your stack.
- Applications10
- Users25
- Reports / month2,000,000
Everything in Start, plus:
- Alerting to six channels
- Unlimited alerts
- API & MCP
With our workflow fully integrated, every website is wired to the right team, new scripts are detected automatically and tracked directly in each client's Slack channel. It has streamlined our entire process.
Built to be resold
The client-facing layer is included: reports, alerts and exports you can hand straight to your clients.

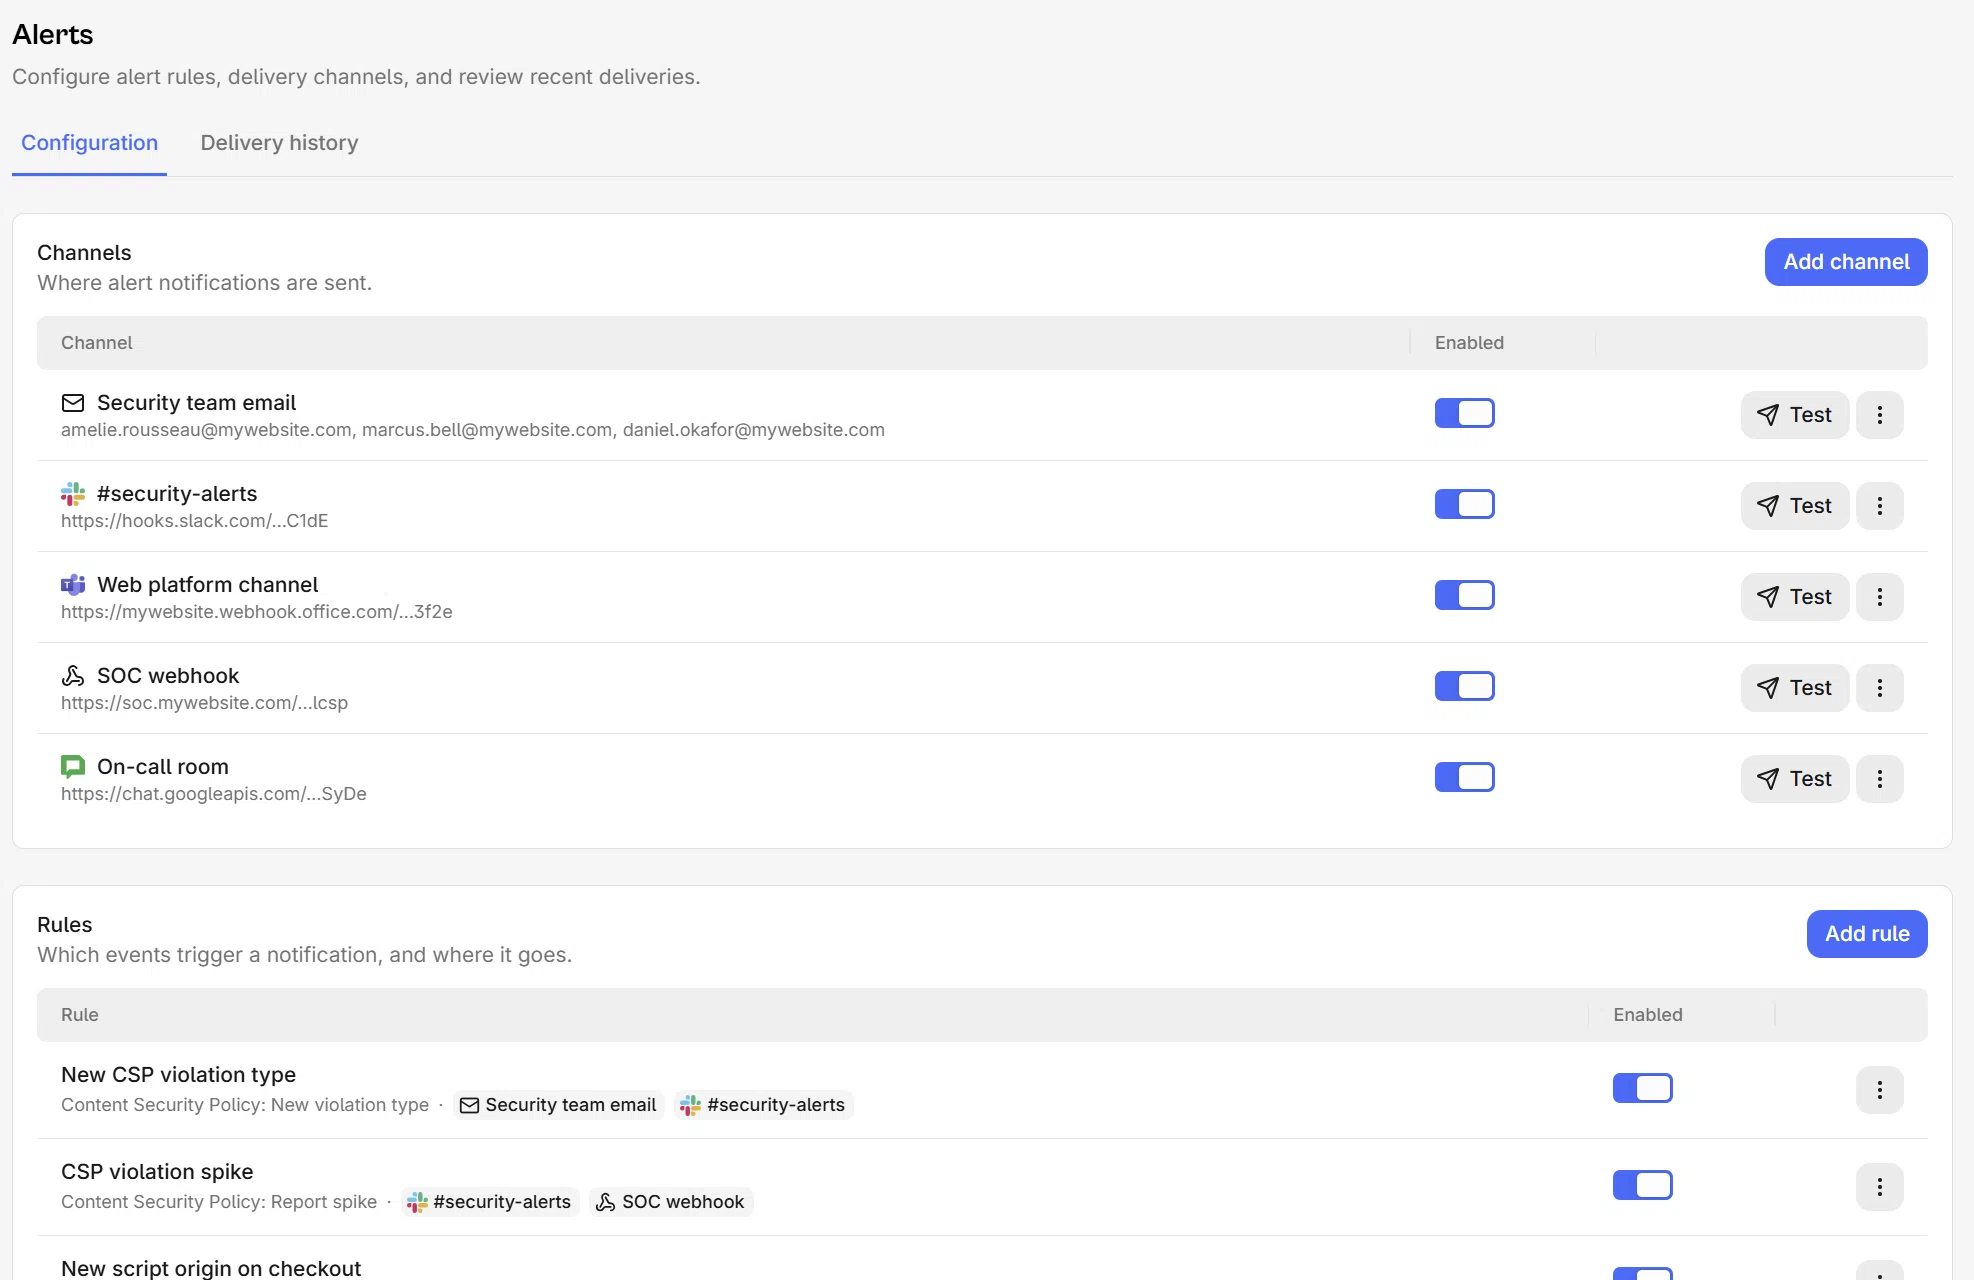
Each client alerted in their own channel
Add a channel per client, Slack, Teams, Google Chat, Telegram, email or webhook, then choose which events reach it. A new script origin on a checkout page lands with the people who own that site.
Evidence you can forward
Payment-page script inventory and PCI DSS exports, ready to hand to the client.
Scans and alerting included
Automated scanning and alerting on six channels ship with Business. CVE detection arrives with Scale.
API and MCP
Pull anything into your own tooling and reports, or drive it with AI.
FAQ
Frequently asked questions
Running client-side security for a portfolio, answered.
Put your portfolio under watch this afternoon.
Start with one client site, add the rest when you're convinced.