Get started
Build a Permissions-Policy from your reports. Pick a period and a preset, grant each feature to your pages and frames, then deploy in report-only mode.
Last update:
This page takes you from the reports your website already collects to a Permissions-Policy deployed in report-only mode, then enforced.
Review every grant, and deploy in report-only first
The builder grants each feature to the pages and frames that browsers reported using it. Anyone who knows your reporting endpoint can send reports to it, so review the grants before you deploy, starting with the features granted to another origin.
Always deploy a new policy with the Permissions-Policy-Report-Only header first. Switch to Permissions-Policy only once a week or more of reports shows that nothing your pages need would be blocked.
Before you begin
Make sure you have:
- A website that sends reports to CentralCSP. The Permissions Policy reports page shows what the builder learns from. If it shows no data, the builder still works: start from a preset and grant features by hand. Refer to Connect your site.
- Access to the server, framework, or content delivery network (CDN) configuration that sets your response headers.
- A list of the iframes your pages embed on purpose, such as a payment form, a video player, or a map.
Decide how long a period to learn from before you start. A longer period catches pages that few visitors open, such as checkout or account settings.
Keep the tab open until you export
The builder saves nothing. The step, the period, and the chosen preset stay in the page address, but your grant and reject decisions, and a policy you paste, live only in the open page. Reloading or closing the tab clears them.
1. Choose the reports to learn from
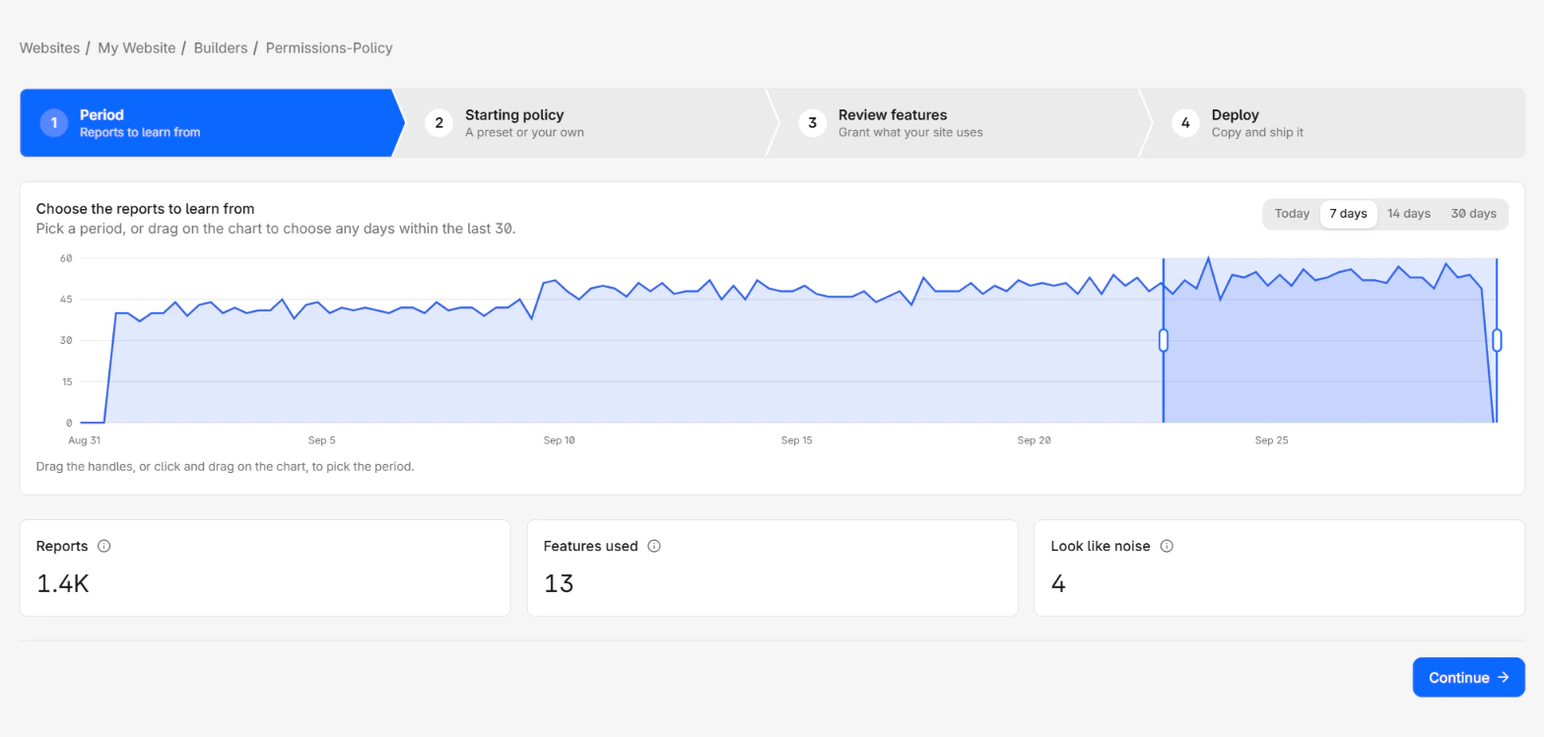
To choose the period:
- In the website sidebar, go to Builders > Permissions-Policy.
- On the Period step, select Today, 7 days, 14 days, or 30 days. For any other range within the last 30 days, drag across the report chart instead.
- Check the three counters: Reports, Features used, and Look like noise.
- Select Continue.
The default period is 7 days. Today is the current calendar day in your timezone, not the last 24 hours. A website that sends a very large volume of reports is limited to 7 days at a time. On such a website the 14 days and 30 days options are hidden. If a period holds too many reports to read in time, the page asks you to pick a shorter period.
If the period holds no reports, the page says Browsers sent no Permissions-Policy reports in this period. Pick a longer period, or continue with a preset.
2. Pick a starting policy
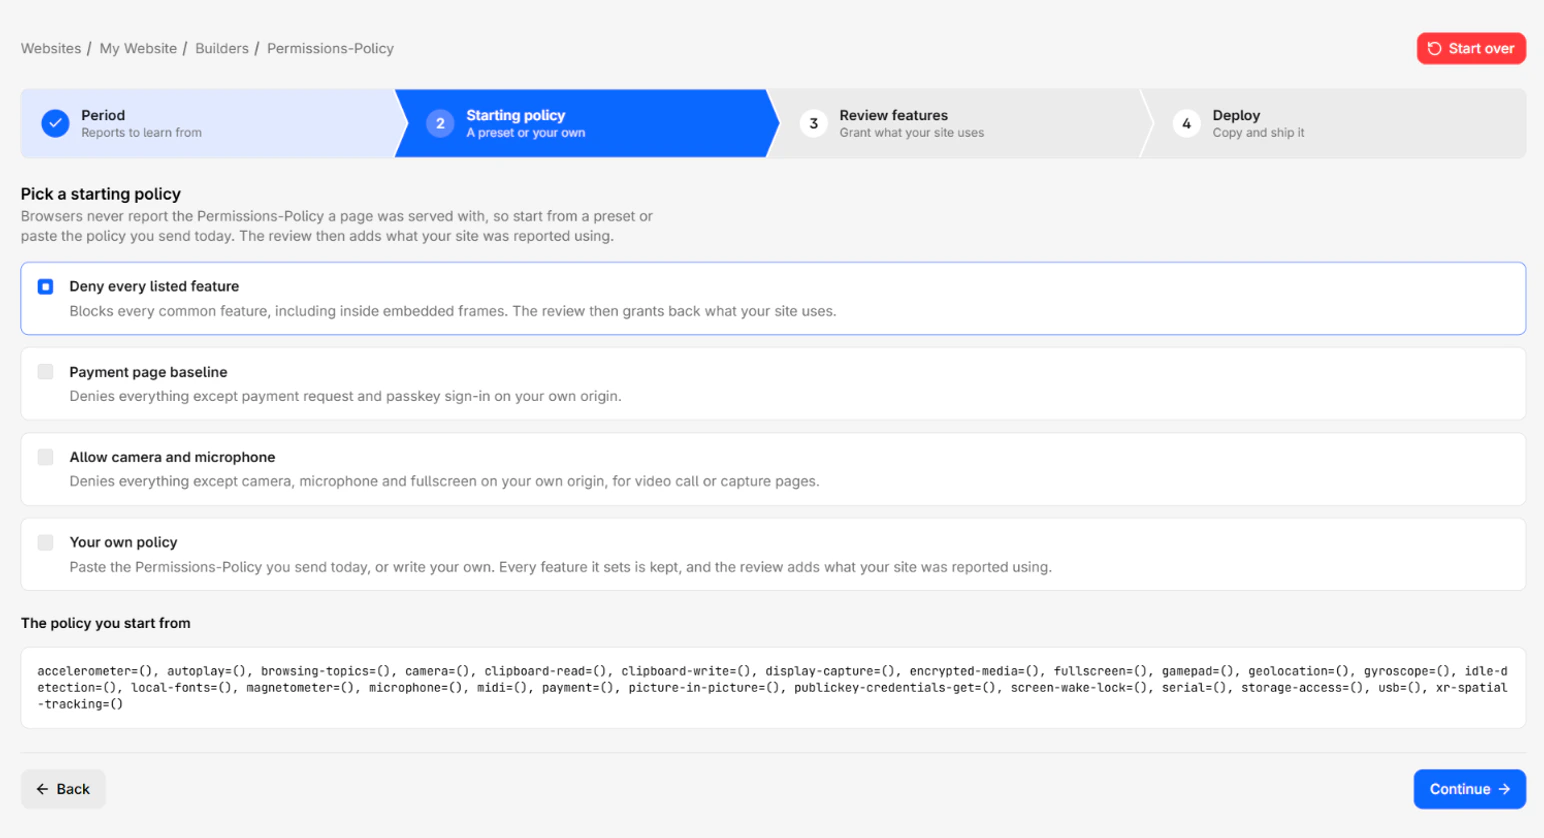
Browsers never report the Permissions-Policy a page was served with, so the builder cannot detect yours. You start from a preset, or from the policy you paste.
To pick the starting policy:
- On the Starting policy step, select one option:
- Deny every listed feature: The default. Denies all 25 features of the catalog, including inside embedded frames.
- Payment page baseline: Denies everything except payment request and passkey sign-in on your own origin.
- Allow camera and microphone: Denies everything except camera, microphone, and fullscreen on your own origin, for video call or capture pages.
- Your own policy: Paste the Permissions-Policy value you send today, without the header name, or write your own.
- Check the header value under The policy you start from.
- Select Continue.
If the builder cannot read any feature from a pasted value, the panel says so. For the exact value of each preset, refer to Starting presets.
3. Review the features
The table lists every feature of the policy you are building, with one row for your own pages (self) and one for each frame origin. Each row is already decided, with what your pages and frames used granted, and noise and third-party-only features rejected.
To review the table:
- On the Review features step, set the flag filter to From frame.
- Check each frame origin. Keep the ones you embed on purpose, such as your payment provider, and select Reject on any origin you do not recognize.
- Set the flag filter to Noise. If a noise row is a feature your site really uses, select Add.
- Set the flag filter to Third-party script. These rows start rejected. To see which scripts called the feature, select the row, then grant it only if you trust that script with the feature.
- (Optional) Select Reject on features you are sure your pages no longer need.
- Select Continue.
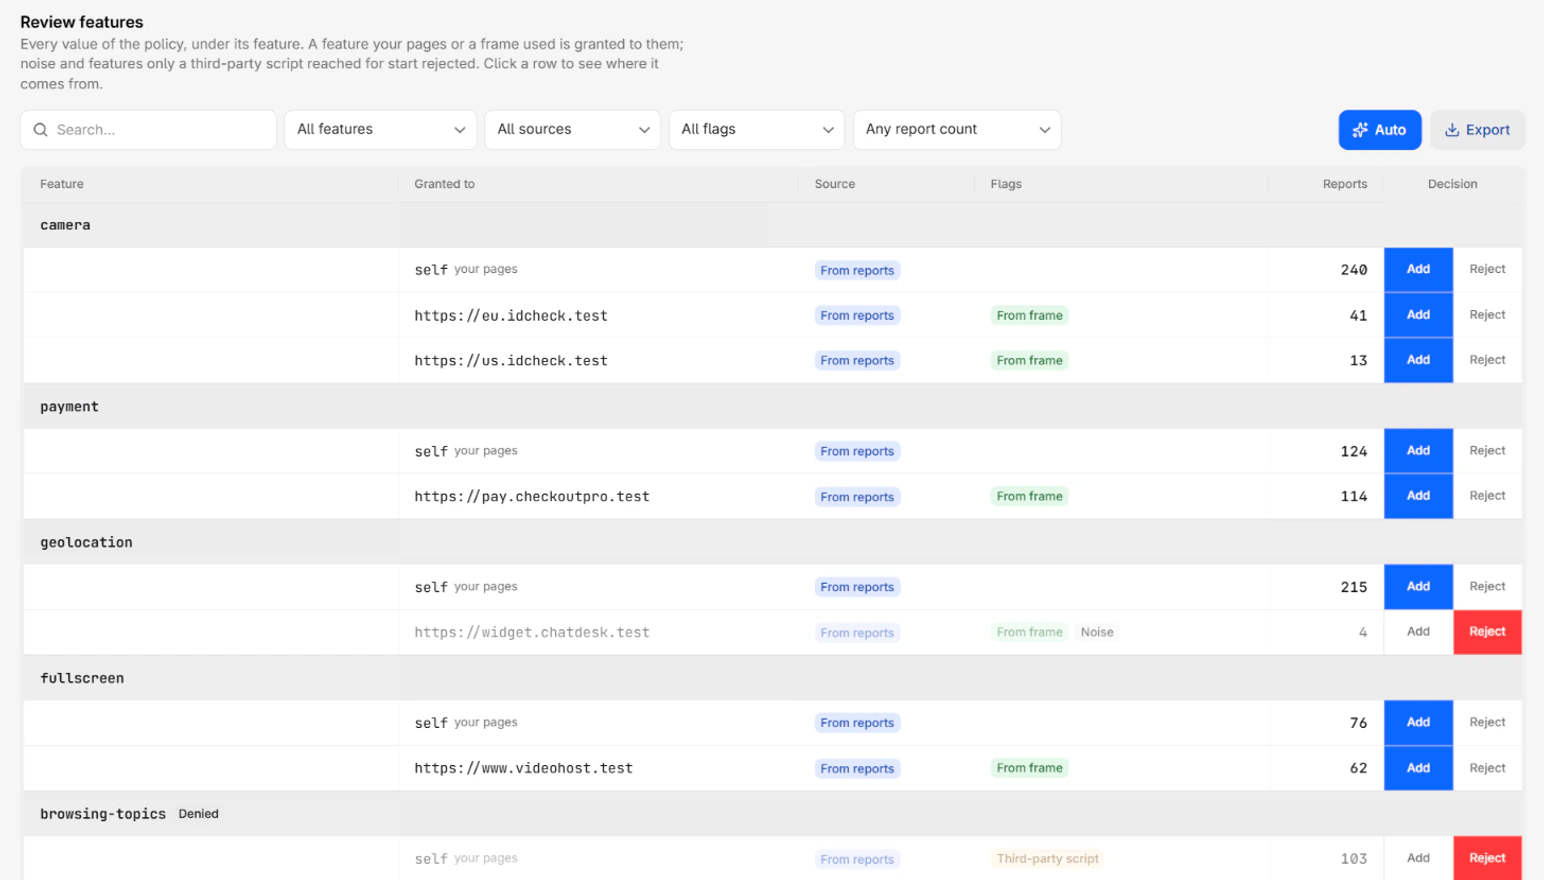
A feature marked Denied has nothing granted, so the header writes it as (). To put every decision back to the builder's recommendation, select Auto. For each column, flag, and filter, refer to Review table.
4. Deploy in report-only mode
To deploy the policy:
- On the Deploy step, leave the mode on Report-only.
- In the code block, copy both headers, or select Export as TXT to download both headers in a text file. The export is recorded in the audit log.
- If the page shows Frames need their allow attribute too, you granted a feature to a frame's origin. Keep the
allowattribute on that iframe, as it is today. - Add both headers to every HTML response your site returns.
The headers look like this example. The first declares the endpoint:
Reporting-Endpoints: centralcsp="https://MyEndpoint.report.centralcsp.com", default="https://MyEndpoint.report.centralcsp.com"The second carries the policy. The builder writes it on one line; it is split here for reading:
Permissions-Policy-Report-Only:
    accelerometer=(),
    autoplay=(),
    browsing-topics=(),
    camera=(self),
    clipboard-read=(),
    clipboard-write=(self),
    display-capture=(),
    encrypted-media=(),
    fullscreen=(self "https://video.example.com"),
    gamepad=(),
    geolocation=(self),
    gyroscope=(),
    idle-detection=(),
    local-fonts=(),
    magnetometer=(),
    microphone=(),
    midi=(),
    payment=(self "https://pay.example.com"),
    picture-in-picture=(),
    publickey-credentials-get=(),
    screen-wake-lock=(),
    serial=(),
    storage-access=(),
    usb=(),
    xr-spatial-tracking=()
The policy has no report-to parameter. Its reports go to the default endpoint that the Reporting-Endpoints header declares.
Granting payment to https://pay.example.com in the header is only half of the delegation. The iframe must still name the feature in its allow attribute (refer to how the header relates to the iframe allow attribute):
<iframe src="https://pay.example.com/checkout" allow="payment"></iframe>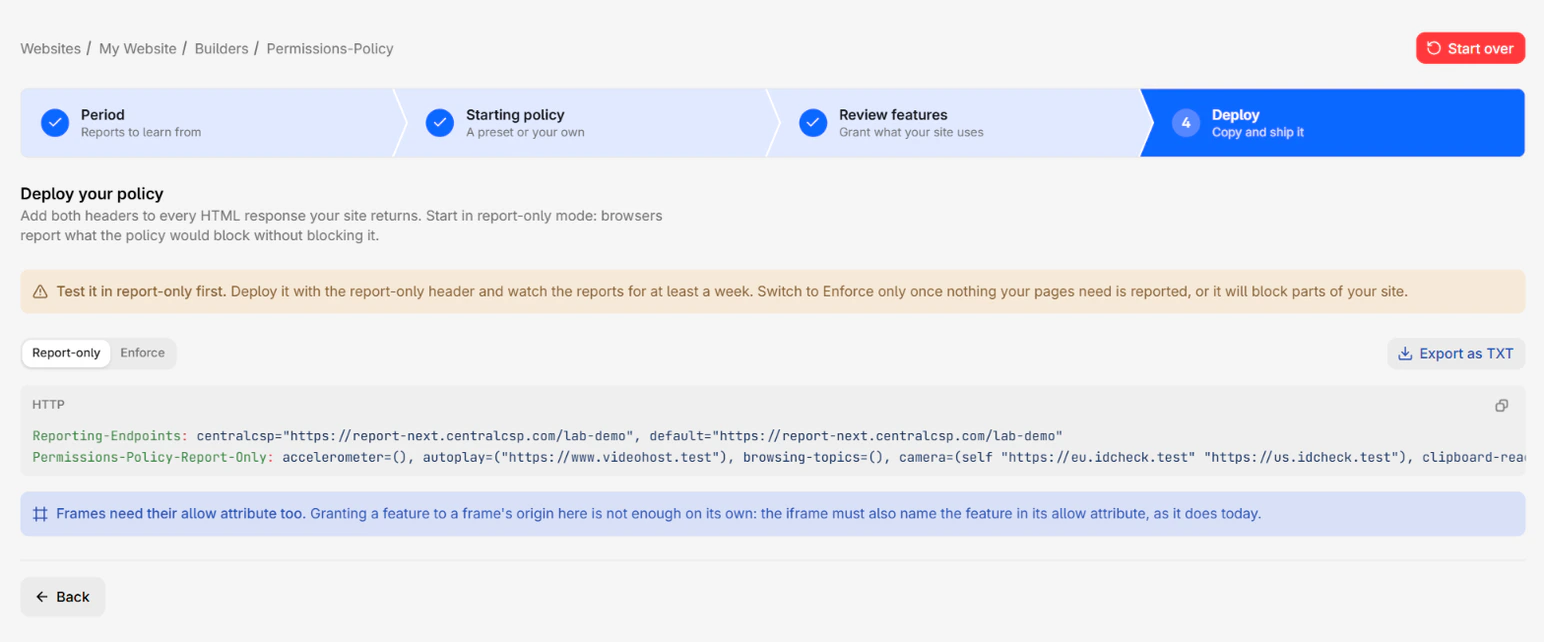
Browsers now report the features the policy would block, without blocking them.
5. Switch to enforce mode
To enforce the policy:
- Watch the Permissions Policy reports page for at least a week. Each violation now means the policy would block a feature your pages used, and each potential violation means a frame asked for a feature the policy would deny.
- When nothing your pages need shows up in the reports, run the builder again on that week. The builder cannot detect the policy you deployed, so select Your own policy and paste it.
- On the Deploy step, select Enforce.
- Replace the report-only header with the
Permissions-Policyheader.
Browsers now block the features the policy does not grant.
Next steps
Overview
Generate a Permissions-Policy header from the reports browsers send. Grant camera, payment, and other features to your pages and frames, then deploy.
Review table
The Permissions-Policy builder review table decides which features your pages and frames may use. Columns, flags, defaults, filters, and details.