

Audit logs
A record of admin actions in the workspace, kept until the account is deleted and never edited.
Last update:
Audit logs records administrative actions taken in this workspace, and only workspace Admin members can read it.
Entries are never edited or deleted. Unlike browser reports, which expire after 90 days, audit entries are kept until the account is deleted.
An automated event shows System as the actor rather than a person. Each entry carries the action key, the target and its id, the event id, and any additional metadata, which is what you need when correlating with your own logs.
Script review decisions are the exception. Justifications and rejections are recorded in the compliance change ledger rather than here, and that ledger is the PCI DSS artefact for script decisions. For more information, refer to Justifying scripts.
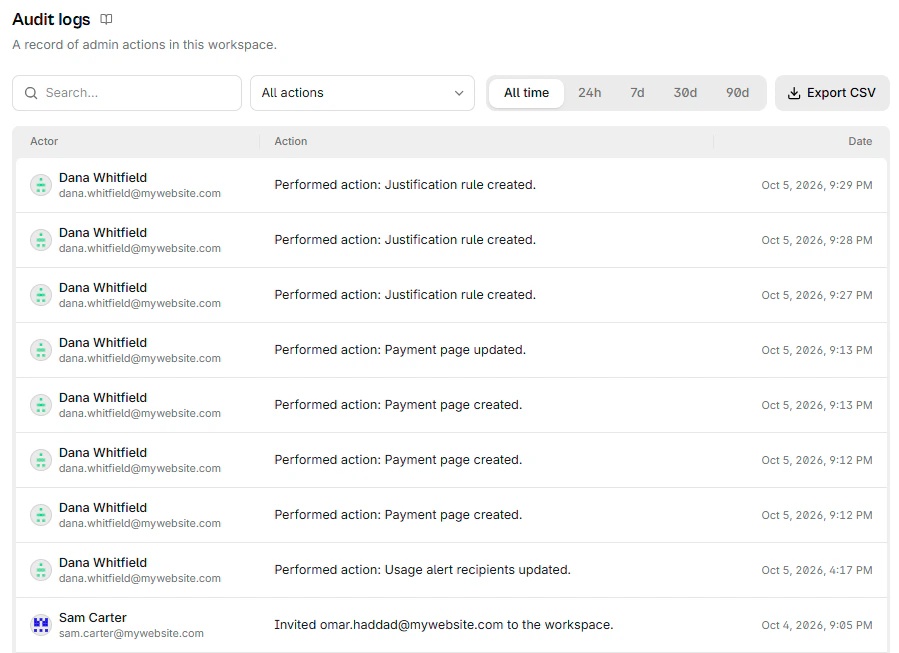
Each row carries an actor, an action, and a timestamp:
Exports
Every export of workspace data adds an entry, so you can see who took data out of CentralCSP and when. Each kind of export has its own action key:
| Action | Recorded when |
|---|---|
reports.exported | Someone exports browser reports from the report explorer |
inventory.exported | Someone exports the script inventory |
technologies.exported | Someone exports the Technologies inventory |
compliance.evidence_exported | Someone exports the PCI DSS evidence pack |
scan.report_exported | Someone exports a scan report |
audit_log.exported | Someone exports the audit log itself |
csp_policy.exported | Someone exports the headers from the CSP builder as TXT |
csp_sources.exported | Someone exports the CSP builder review table as CSV |
permissions_policy.exported | Someone exports the headers from the Permissions-Policy builder as TXT |
permissions_policy_values.exported | Someone exports the Permissions-Policy builder review table as CSV |
connection_allowlist.exported | Someone exports the headers from the Connection-Allowlist builder as TXT |
connection_allowlist_destinations.exported | Someone exports the Connection-Allowlist builder review table as CSV |
A header export (csp_policy.exported, permissions_policy.exported, connection_allowlist.exported) keeps the mode (report-only or enforce), the exported policy (its first 4,000 characters), and its SHA-256 hash. A review table export (csp_sources.exported, permissions_policy_values.exported, connection_allowlist_destinations.exported) keeps the row count and the filters that were active.
Next steps
Two-factor enforcement
Require every workspace member to have two-factor authentication. What happens to members who do not, and the one prerequisite before turning it on.
Data retention
Browser reports are kept 90 days, fixed and not configurable. Compliance decisions and audit logs are kept until the account is deleted.