Script inventory
The review queue for scripts observed on your payment pages, for PCI DSS 6.4.3 and 11.6.1. The four tabs, the statuses, and what each script records.
Last update:
PCI DSS > Script inventory holds every script observed on a page matching a payment-page pattern that is turned on, each with a review status. It is the working queue for requirements 6.4.3 and 11.6.1.
PCI DSS monitoring requires a plan that includes compliance. Compare plans on the pricing page or under Settings > Billing.
The scripts themselves come from the script inventory CentralCSP builds from CSP hash reports. This page is that inventory narrowed to payment-page scope, with statuses, justifications, and an audit trail attached.
If the page is empty, the cause is almost always scope rather than reporting. For more information, refer to Payment pages.
The four tabs
The inventory is split across four tabs:
| Tab | Shows |
|---|---|
| Origins | One row per origin serving scripts in scope |
| Scripts | The full inventory, filterable by any status |
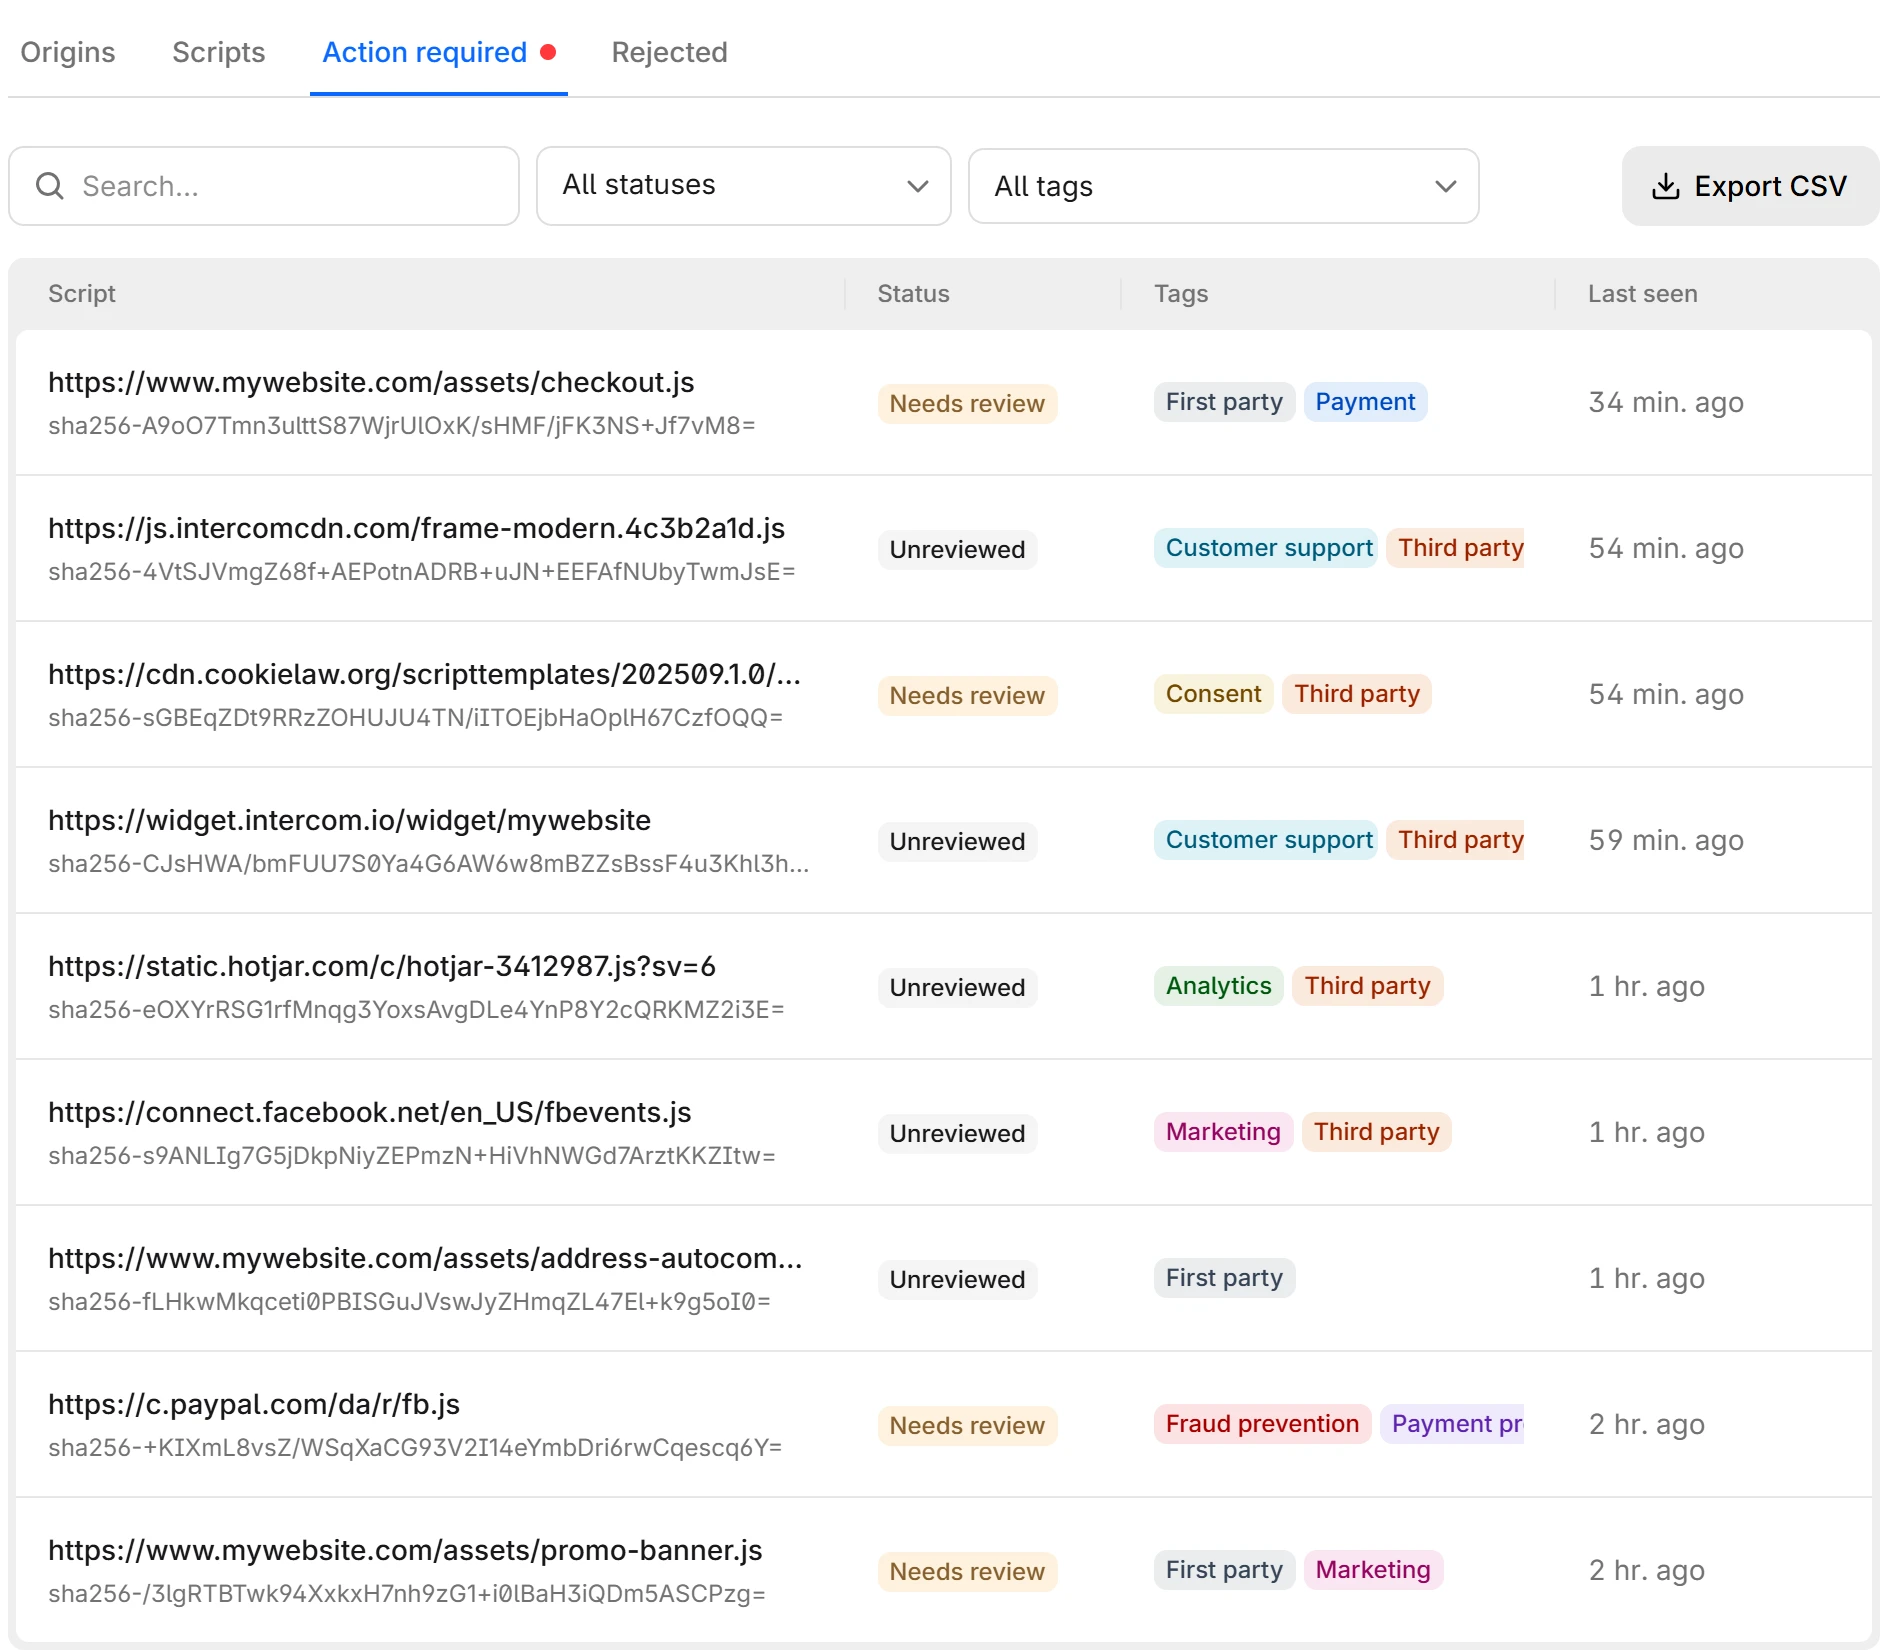
| Action required | Your work queue, holding only Unreviewed and Needs review |
| Rejected | Only scripts marked rejected |
Select an origin on the Origins tab to filter Scripts by it. Work from Action required. It is the only tab whose emptiness means something, and a red dot on it shows that scripts are waiting for a decision. Rules can shorten that queue before you reach it. For more information, refer to Inventory rules.
Retired scripts do not appear on any tab.
The Action required tab holds a mix of statuses:
Review statuses
Every script in scope carries one status:
| Status | Meaning |
|---|---|
| Unreviewed | Detected, nobody has decided |
| Needs review | Was justified, and the hash has changed since |
| Justified | Authorized at its current hash |
| Rejected | Judged not to belong on a payment page |
Needs review is the status that does the work in requirement 11.6.1. A justification is pinned to the hash it was made against. When content at that URL changes, the script comes back to you instead of staying quietly approved.
The evidence PDF prints these as Pending review, Hash changed, Authorized, and Rejected.
What is recorded per script
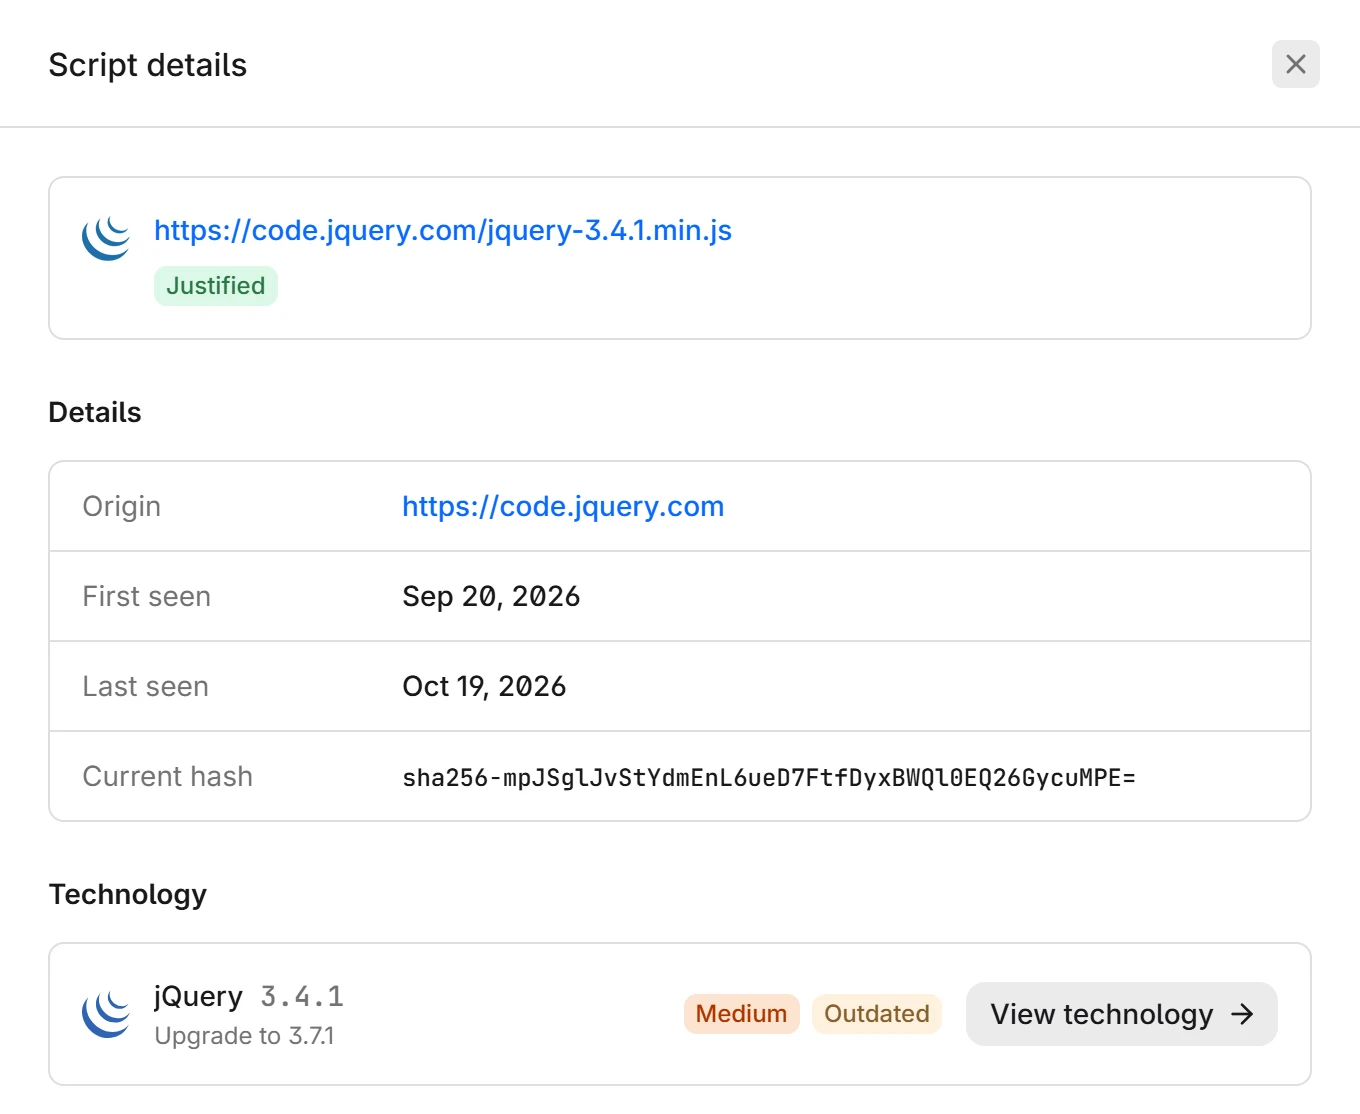
Each script carries its origin, first and last seen, current hash, tags, the current review decision, and the full history.
Two things there are worth knowing. Pages lists the document URLs it was seen on, which answers scope questions directly. Hash history lists every hash with first and last seen, which is how you tell a routine release cadence from an unexpected change.
When the script carries a library that Technologies recognizes, a Technology section names the library, its version, and its status, with the recommended upgrade, or Find an alternative when no maintained release exists. View technology opens it on the Technologies page, with its vulnerabilities. That tells you whether the script you are about to justify ships a known vulnerability.
On a plan without Technologies, the section says that Technologies identifies the library a script carries and its known vulnerabilities, on higher plans. The workspace owner gets a View plans link to the billing page, and other members are asked to contact the owner.
Making decisions from here is covered in Justifying scripts.
Refresh inventory
Managers get a Refresh inventory button, rate-limited to once per 30 seconds. For more information on roles, refer to Access control. Reconciliation also runs hourly and immediately after any scope or rule change, so you rarely need it. For more information, refer to Reconciliation.
Export the script inventory to CSV
The toolbar exports the current view, honouring your filters, with no row limit. It includes the justification text, both hashes, who decided and when, and the tags.
Use it to work through a large inventory in a spreadsheet, or to share one with someone who has no dashboard access. The Viewer role is enough.
For a full audit package including the ledger, use the evidence export instead.